In the dynamic landscape of modern software development, Application Programming Interfaces (APIs) have emerged as the linchpin for seamless communication between different software systems. As an API interface supplier, I'm often confronted with a pivotal question from our clients: Can an API interface support multiple authentication methods? This blog post aims to delve deep into this query, exploring the technical feasibility, benefits, challenges, and real - world implications of enabling multiple authentication methods in an API interface.
Technical Feasibility
From a technical perspective, an API interface can indeed support multiple authentication methods. Modern programming languages and frameworks offer a plethora of tools and libraries that facilitate the implementation of various authentication mechanisms. For instance, in Python, the Flask - RESTful framework can be combined with libraries like Flask - HTTPBasicAuth for basic authentication and Flask - JWT for JSON Web Token (JWT) authentication.
Let's take a closer look at some common authentication methods that an API can support:

- Basic Authentication: This is one of the simplest forms of authentication. It involves sending a username and password with each API request, typically encoded in Base64. While it's easy to implement, it has security limitations, such as the risk of password interception if not used over a secure connection.
- OAuth: OAuth is an open - standard authorization protocol that allows users to grant third - party applications limited access to their resources without sharing their credentials. It's widely used in social media platforms and other web services. An API can support different versions of OAuth, like OAuth 1.0a and OAuth 2.0, depending on the requirements.
- JSON Web Tokens (JWT): JWT is a compact, URL - safe means of representing claims to be transferred between two parties. It consists of a header, a payload, and a signature. APIs can use JWT for authentication and authorization, as it can carry user information and permissions.
By leveraging the capabilities of modern programming languages and security libraries, an API can be designed to handle multiple authentication methods simultaneously. This means that different clients or use cases can choose the most appropriate authentication mechanism based on their security needs and technical capabilities.
Benefits of Supporting Multiple Authentication Methods
- Enhanced Security: Different authentication methods have different security strengths. By supporting multiple methods, an API can offer a more robust security model. For example, a high - security application might use OAuth for its users, while a less - sensitive internal system could use basic authentication. This way, the API can adapt to different security requirements and mitigate the risks associated with a single authentication method.
- Increased Compatibility: Different clients may have different preferences or limitations when it comes to authentication. Some legacy systems may only support basic authentication, while modern mobile applications may be more inclined to use JWT. By supporting multiple methods, an API can be more compatible with a wider range of clients, expanding its market reach.
- Flexibility for Developers: Developers can choose the authentication method that best suits their application's architecture and requirements. This flexibility allows for more efficient development and better integration with other systems. For example, a developer working on a data - sharing application might choose to use OAuth to allow users to access their data from different platforms securely.
Challenges of Supporting Multiple Authentication Methods
- Complexity of Implementation: Implementing multiple authentication methods in an API can be a complex task. It requires careful planning and coding to ensure that each method works correctly and that there are no conflicts between them. For example, handling different error messages and response formats for each authentication method can be challenging.
- Security Management: With multiple authentication methods, there is a greater risk of security misconfigurations. Each method has its own security requirements and best practices, and ensuring that all of them are properly implemented and maintained can be difficult. For instance, if an API supports both basic authentication and JWT, it's crucial to ensure that the basic authentication credentials are not compromised, and the JWTs are properly signed and verified.
- Documentation and Training: Providing clear documentation and training for developers on how to use each authentication method is essential. However, with multiple methods, the documentation can become more complex, and developers may need more time to understand and implement them correctly.
Real - World Implications
In the real world, the ability to support multiple authentication methods can have a significant impact on an API's success. For example, consider a logistics company that provides an API for its partners to access shipment tracking information. Different partners may have different security requirements and technical capabilities. Some large enterprises may prefer to use OAuth for its advanced security features, while smaller businesses may find basic authentication more straightforward.
By offering multiple authentication methods, the logistics company can attract a wider range of partners, increasing its business opportunities. Additionally, it can enhance the security of its API, protecting sensitive shipment data from unauthorized access.
Another example is in the e - commerce industry. An e - commerce API that supports multiple authentication methods can be more appealing to developers of mobile shopping applications. These applications may use JWT for user authentication within the app, while also allowing users to log in using their social media accounts via OAuth. This provides a seamless and secure shopping experience for customers.
Our Approach as an API Interface Supplier
As an API interface supplier, we understand the importance of supporting multiple authentication methods. We have a team of experienced developers who are well - versed in implementing various authentication mechanisms. We follow industry - best practices to ensure the security and reliability of our APIs.
When developing an API for a client, we first assess their security requirements and the capabilities of their target clients. Based on this assessment, we determine which authentication methods are most appropriate and implement them in a way that minimizes complexity and maximizes security.
We also provide comprehensive documentation and support to our clients, helping them understand and use the different authentication methods available. Our goal is to make the integration process as smooth as possible for our clients, enabling them to focus on developing their applications.
Related Products and Services
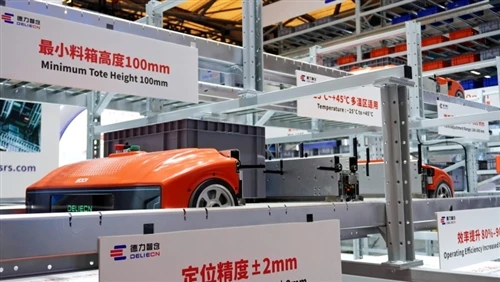
In addition to our API services, we also offer a range of related products that can enhance the functionality and security of your applications. For example, our Tote Transfer Machine can be integrated with your API to automate the movement of totes in a warehouse. This can improve efficiency and reduce the risk of human error.
Our Pallet Four - Way Shuttle Robot is another innovative product that can be integrated with your API. It provides a flexible and efficient way to handle pallets in a warehouse, improving storage density and throughput.
Finally, our Pallet Shuttle Robot Racking system can be integrated with your API to optimize the storage and retrieval of pallets. This can help you make the most of your warehouse space and improve inventory management.
Conclusion
In conclusion, an API interface can support multiple authentication methods, and doing so offers numerous benefits, including enhanced security, increased compatibility, and flexibility for developers. However, it also comes with challenges, such as complexity of implementation and security management.
As an API interface supplier, we are committed to providing high - quality APIs that support multiple authentication methods. We believe that by offering this flexibility, we can help our clients develop more secure and innovative applications.
If you are interested in our API services or any of our related products, we encourage you to contact us for a detailed discussion. Our team of experts is ready to assist you in finding the best solutions for your business needs.
References
- OAuth 2.0 and OpenID Connect (OIDC) in Plain English. Auth0.
- JSON Web Tokens - Introduction. jwt.io.
- RESTful API Authentication Best Practices. Smashing Magazine.